Who is behind the sensor on your nodes
PandoCore runs on your nodes with elevated privileges, which is a good reason to want to know who is behind it.
How we work
Simple solutions. Two Helm charts, controller first, and nothing to label. There are no rules to write and no security hire to make. Every option we add is one more thing that can be set wrong.
First principles. We shipped an injected sidecar, decided it was wrong, and replaced it rather than defend it. The posts arguing for it are still up, with dated notes. The sensor cannot delete a pod: its ClusterRole enforces that.
Patience over launch dates. We published a soak's scoring rules before its results, so the bar could not move. When the architecture changed we withdrew our own favourable figures. The trust center lists what the sensor does badly; the product page says we hold no third-party attestation.
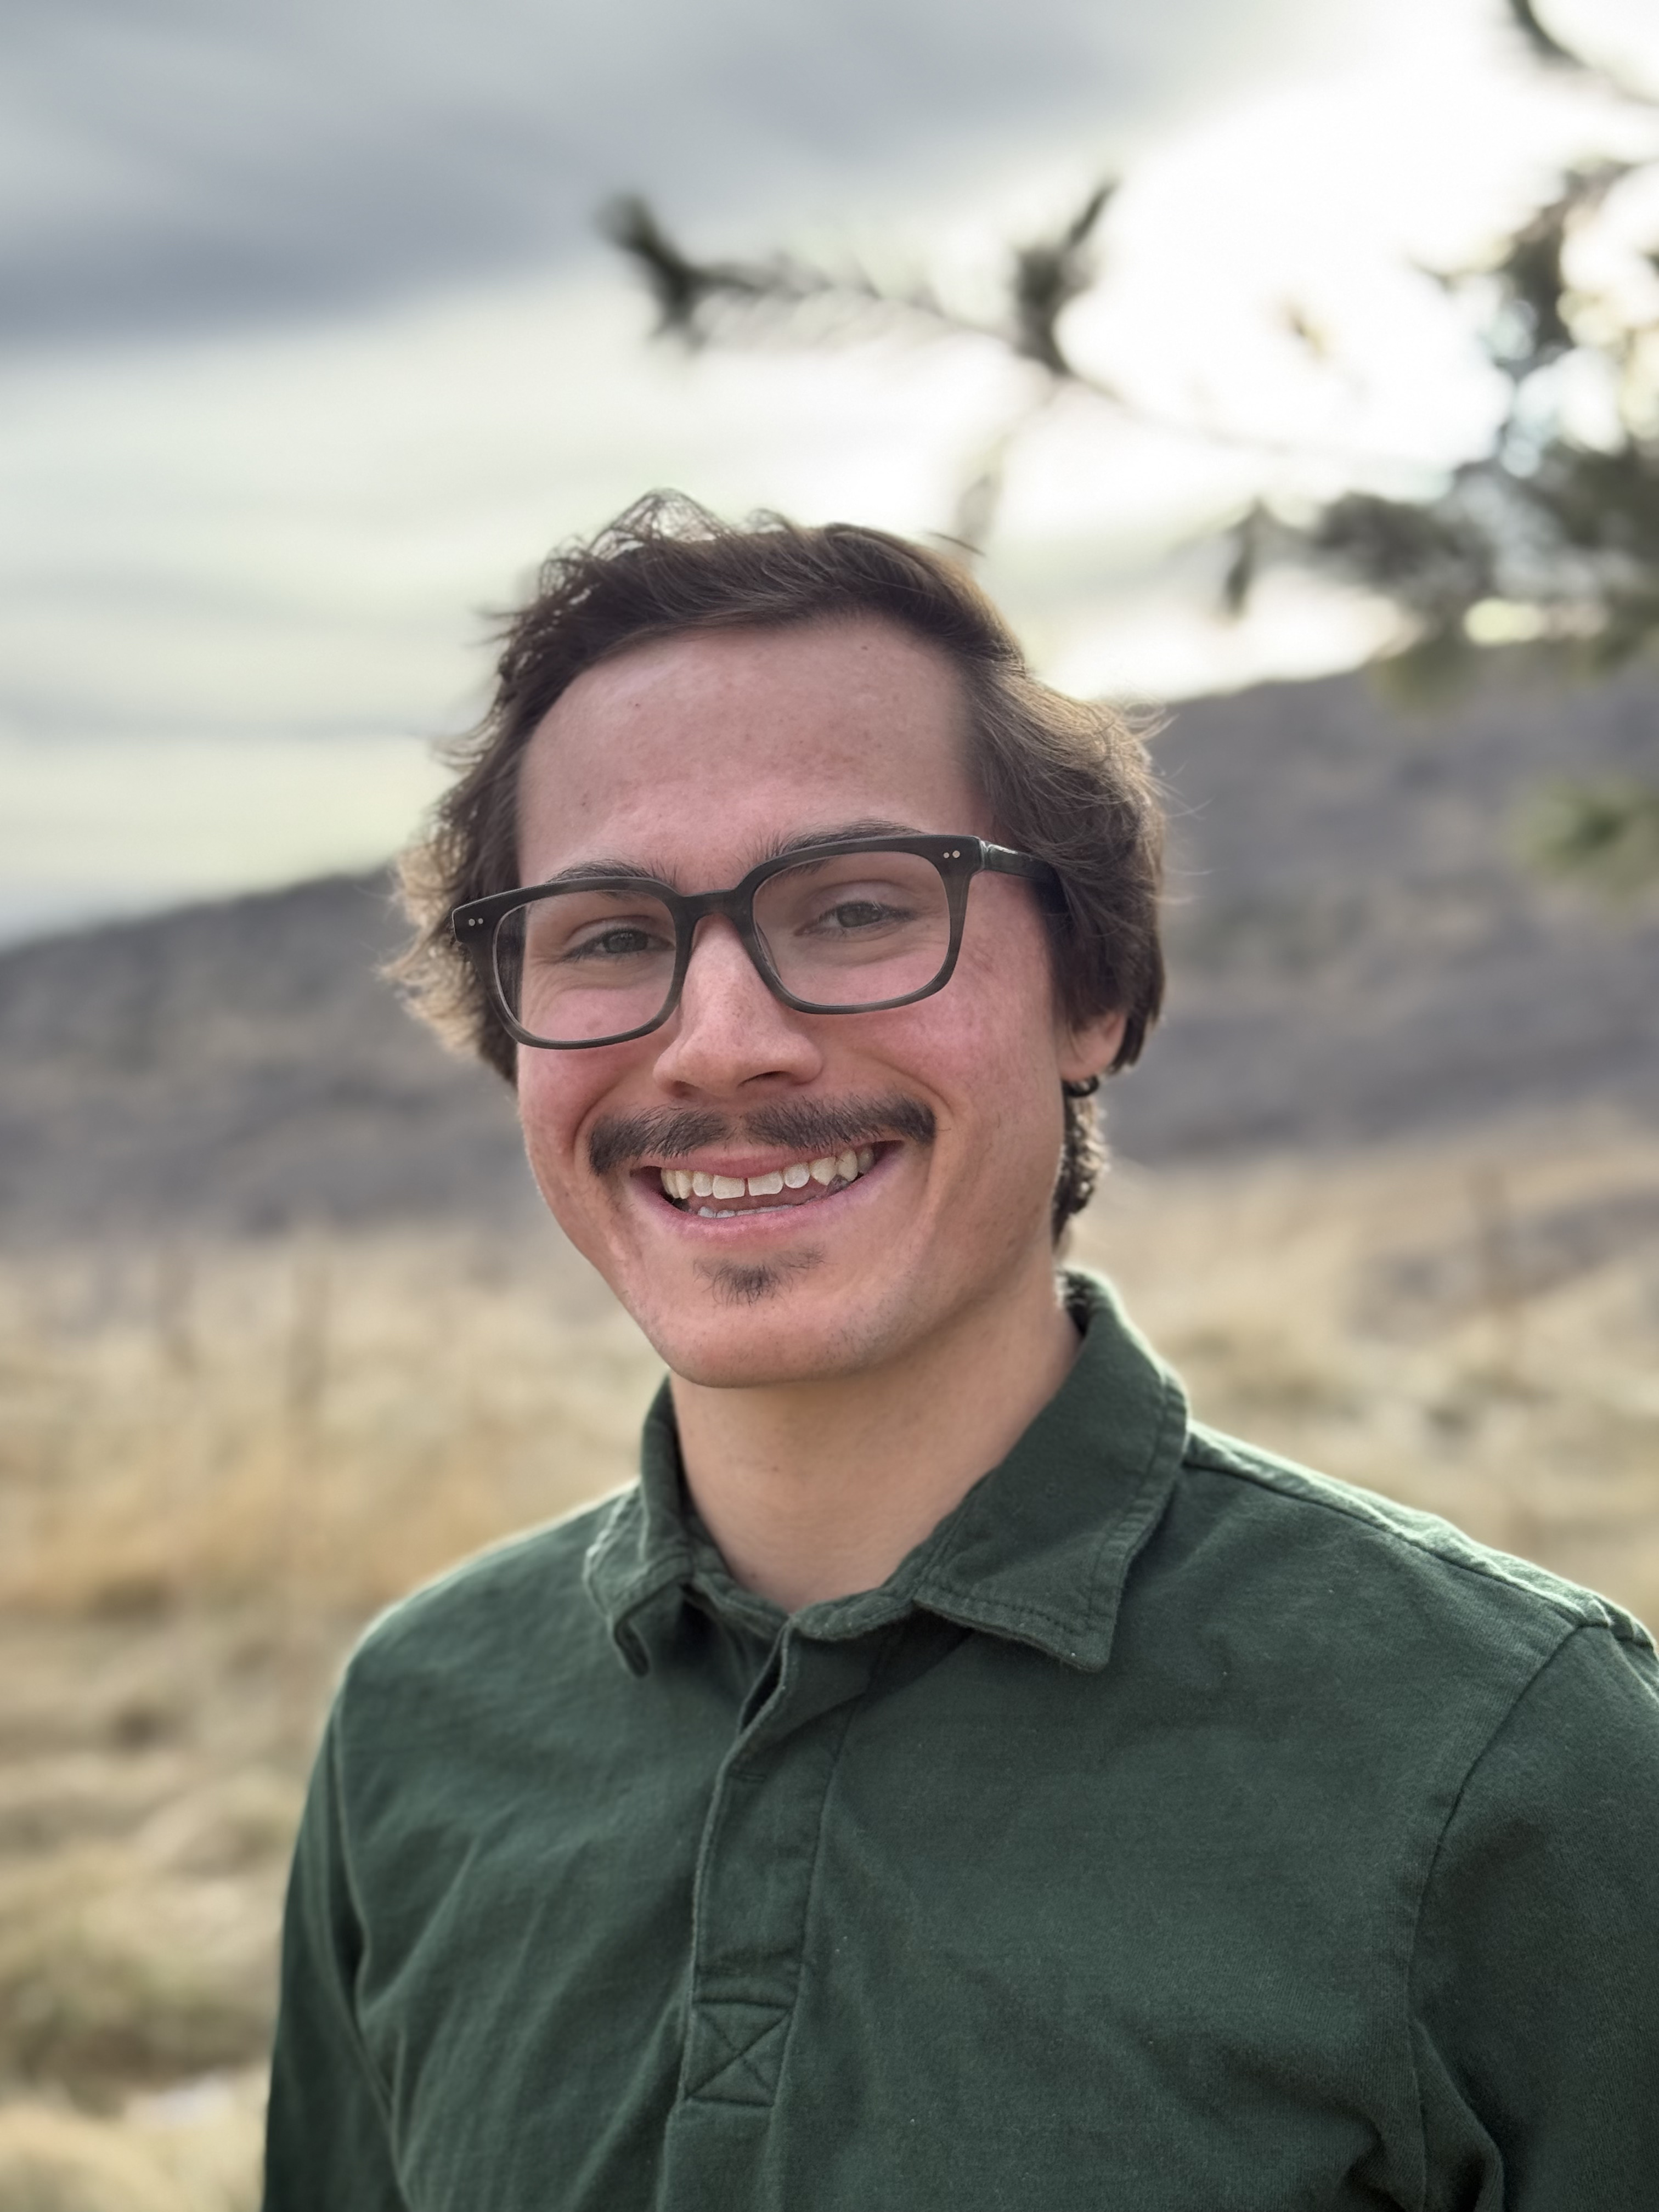
Eliot studied applied physics at Ohio State, focused on mathematics and machine learning. He was CTO at Spex Local from 2021 until it failed in 2022, then Director of Product Engineering at speculo.ai from 2023 to 2025. PandoCore measures a workload's drift from its own normal, which is a mathematics problem before it is a security one.
It is worth being straight about what that background is not. He is not a career security engineer or a cryptographer. The parts where that would matter are published so you can check them: the ClusterRole ships in the chart, the signing key and what the sensor does badly are in the trust center, and the methodology is on the blog.
If you want to look closer, start free or book a call.